Governance, Risk & Compliance for Salesforce

Risk management,
where your team already works.

DefinedGRC extends your Salesforce investment into enterprise risk management. Registers, assessments, resilience and compliance all live in your own Salesforce org, with no new platform to adopt and no data to move.

  • Native to Salesforce Installed in your org
  • Yours to shape Unmanaged package
  • Framework expertise Delivered through our partners
DefinedGRC home dashboard inside Salesforce

How can you resolve a risk if you don't know what you're solving?

Most risk teams are not short of effort. They are short of consistency. The same three problems show up again and again.

Risk lives somewhere else

Spreadsheets, a standalone GRC tool or a shared drive. Your risk data sits away from the systems and people the risks actually affect, and it goes stale.

Inconsistent definitions

Risk events and control assessments are logged vaguely, described differently by each team and captured as narrative rather than insight.

Reactive, not proactive

Teams spend more time interpreting what happened than preventing it from happening again, because the structure to learn from it was never in place.

Built for Salesforce teams

Already on Salesforce? Your risk platform is one install away.

If your people already live in Salesforce, the best place for risk management is alongside everything else they do. DefinedGRC is built natively, not bolted on.

One platform, one login

Risk owners, control owners and executives use the Salesforce they already know. Less training, higher adoption.

Your data stays in your org

Risk records follow your existing security and sharing model. There is no external system holding sensitive data and no integration to maintain.

Extend it with the platform

Use Salesforce reports, dashboards, flows and permissions with your risk data. Your admins can extend DefinedGRC the same way they extend anything else.

Three ways to get started

Use it as it is, make it yours, or build the framework first.

DefinedGRC is an unmanaged package installed into your Salesforce org. Every route starts from the same product, so you choose how much you tailor.

1

Use it as configured

Best if you want to move quickly

Install the package and start working. It arrives already configured with a risk register and taxonomy, RCSA, risk events, indicators, business continuity and compliance tools.

2

Bespoke to your process

Best if you have an established way of working

Because the package is unmanaged, every object, field, flow and Lightning component is yours to change. We can tailor taxonomy, scoring, workflows and screens to match your policies, or build custom components where your needs are unique.

Salesforce licences for your users remain with Salesforce. DefinedGRC runs on the Salesforce licences you already hold.

The product

A consistent risk language, from register to control.

Systems, processes, risks and controls are defined in one unified model, so every team describes and scores risk the same way.

Risk register & standardised taxonomy

Enforce one risk language across the enterprise. Every risk is defined, categorised and scored against your own framework, using an expandable multi-level taxonomy.

  • ✓ Enterprise risk register and libraries
  • ✓ Control inventories and mapping
  • ✓ Dynamic risk calculations
DefinedGRC risk register

Risk & Control Self-Assessment (RCSA)

Map critical business processes and controls with total clarity. Assess inherent and residual risk through multiple lenses, such as lowest control score or overall control effectiveness.

  • ✓ Visualise how each control relates to your risk framework
  • ✓ Assessment items that link risks directly to controls
  • ✓ AI-assisted control suggestions for your team to review
DefinedGRC RCSA manager

Also included: risk events and root cause analysis, key risk, control and performance indicators, policy attestations, governance and action tracking. View the full feature list →

Operational resilience

Continuity plans that are living records, not PDFs.

Embed your Business Impact Analysis and continuity plans in Salesforce, connected to the same processes, systems and risks as the rest of your framework.

Business Impact Analysis & BCP

Understand which processes, systems and resources matter most, and what to do when minutes count.

  • ✓ BIA with system prioritisation and resource impact views
  • ✓ Incident response and crisis playbooks
  • ✓ Dependencies mapped across processes and resources
Business Impact Assessment manager

Indicators that act early

Track key risk, control and performance indicators against thresholds, so breaches are flagged and corrective actions started before they become failures.

Key risk indicators
AI-assisted

AI that helps your risk team, while they stay in control.

AI suggestions support your team's judgement and save time. Your people review, edit and decide.

AI-assisted

Clearer risk definitions

Turn operational descriptions into clear, consistent risk statements, aligned to recognised approaches such as ISO 31000 and COSO.

AI-assisted

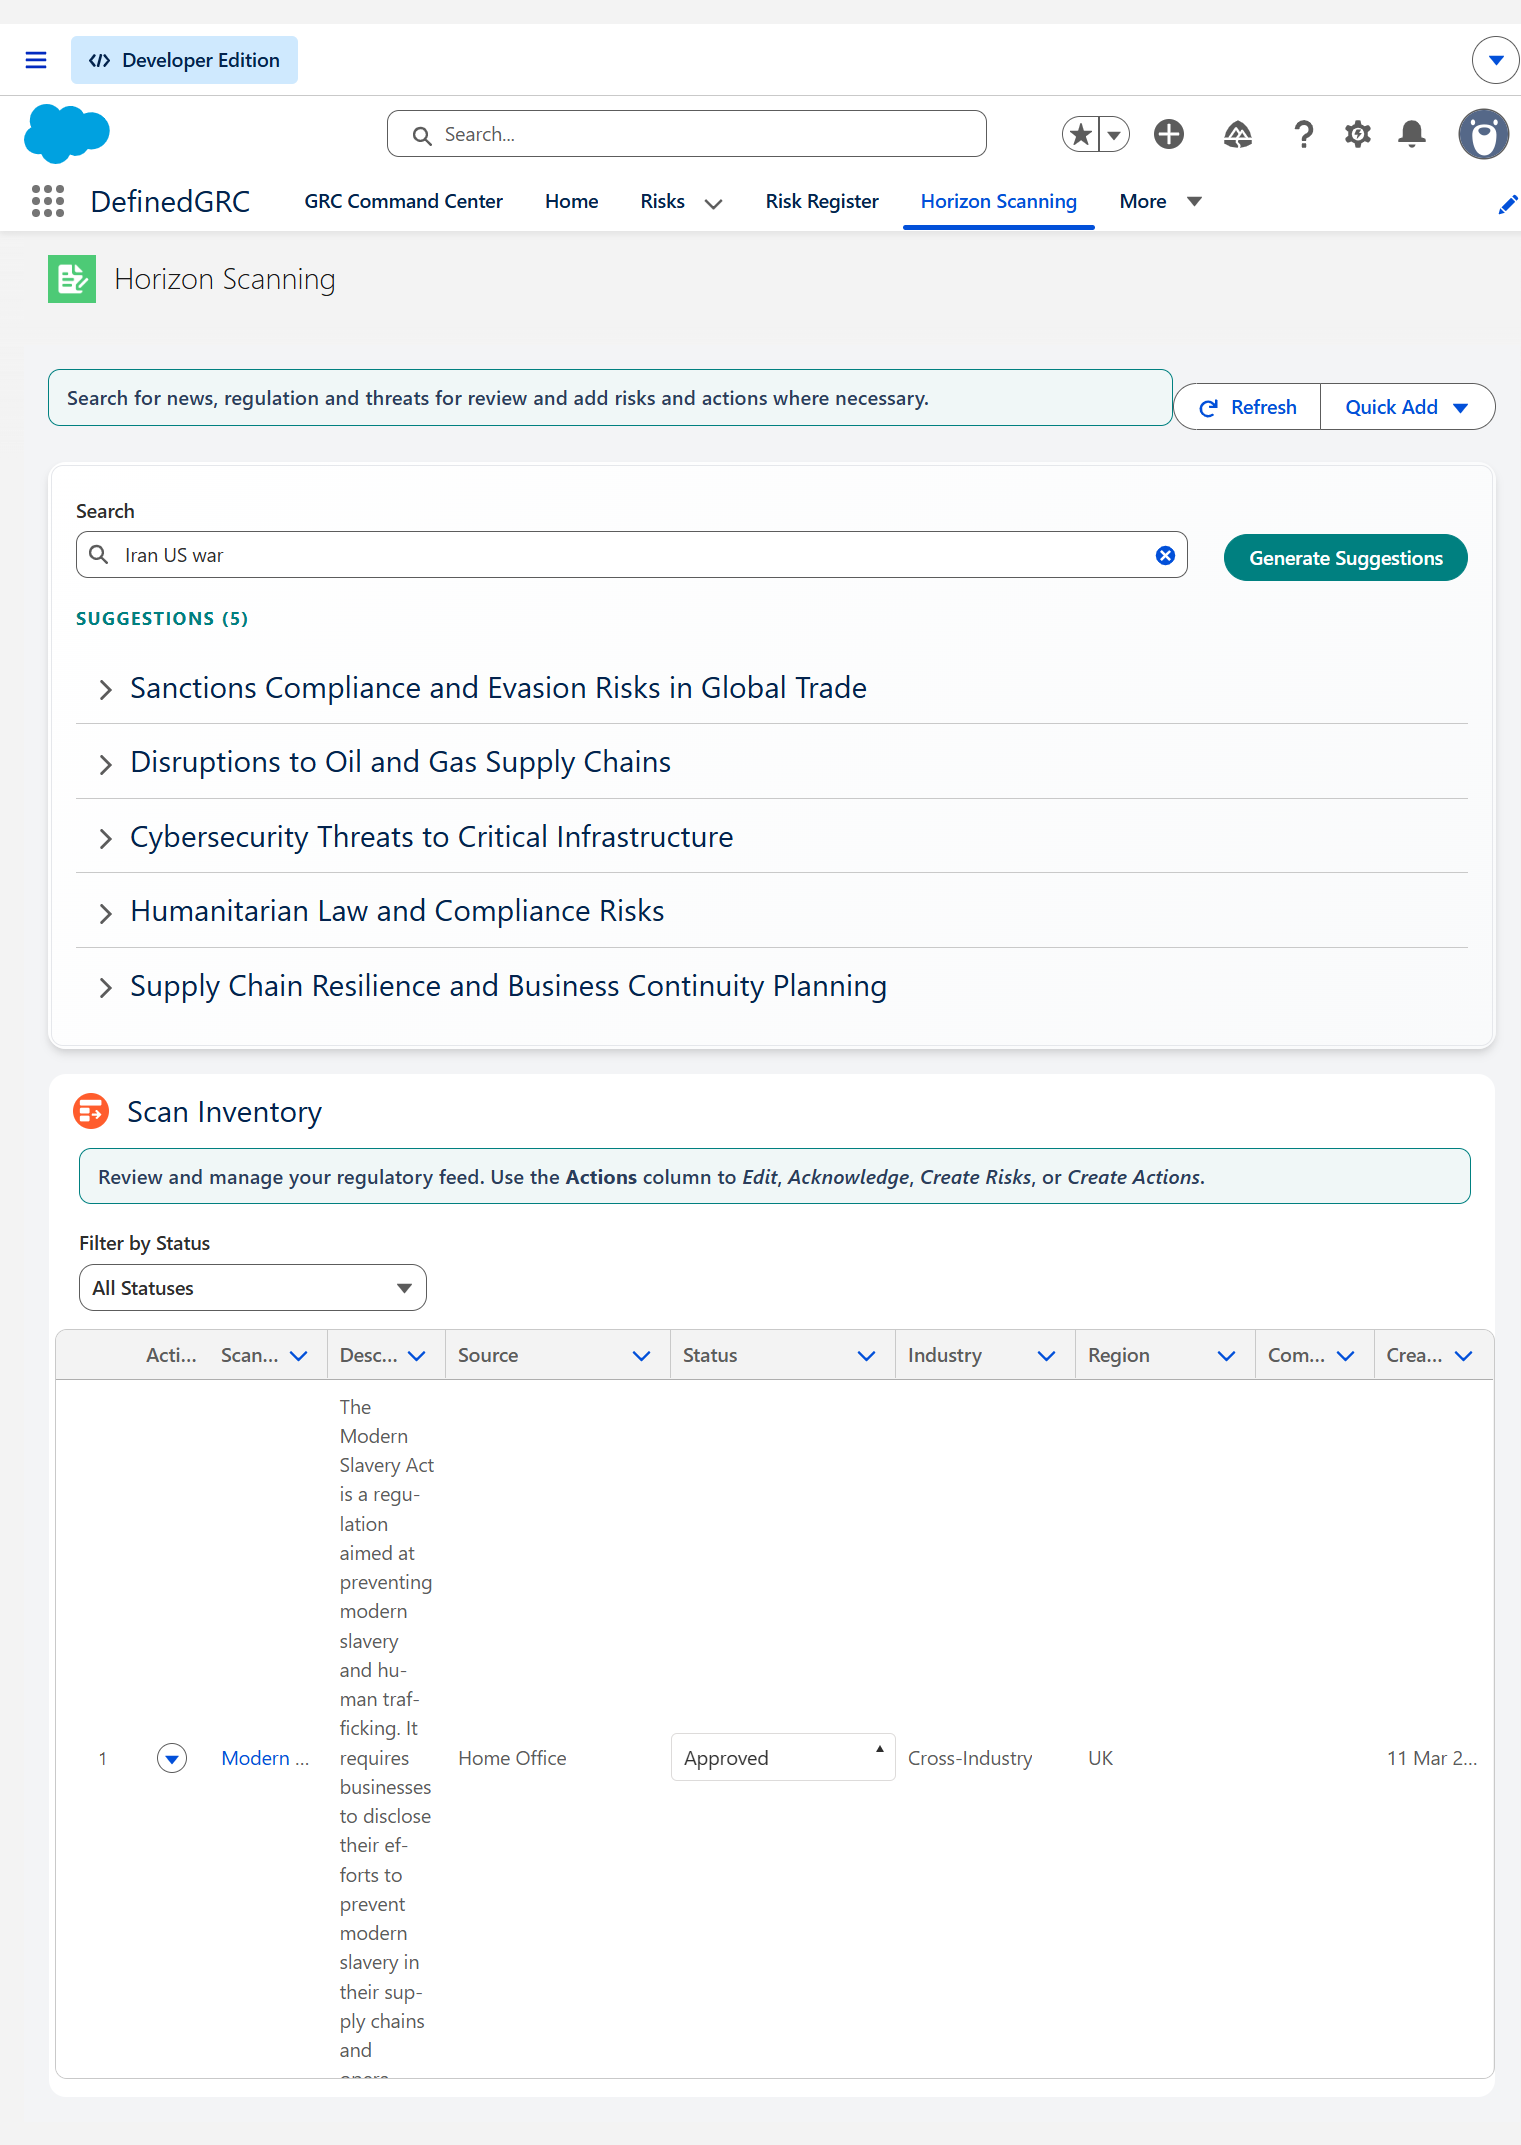
Horizon scanning

Monitor emerging risks, trends and regulatory change, so your framework keeps pace with what is coming.

AI-assisted

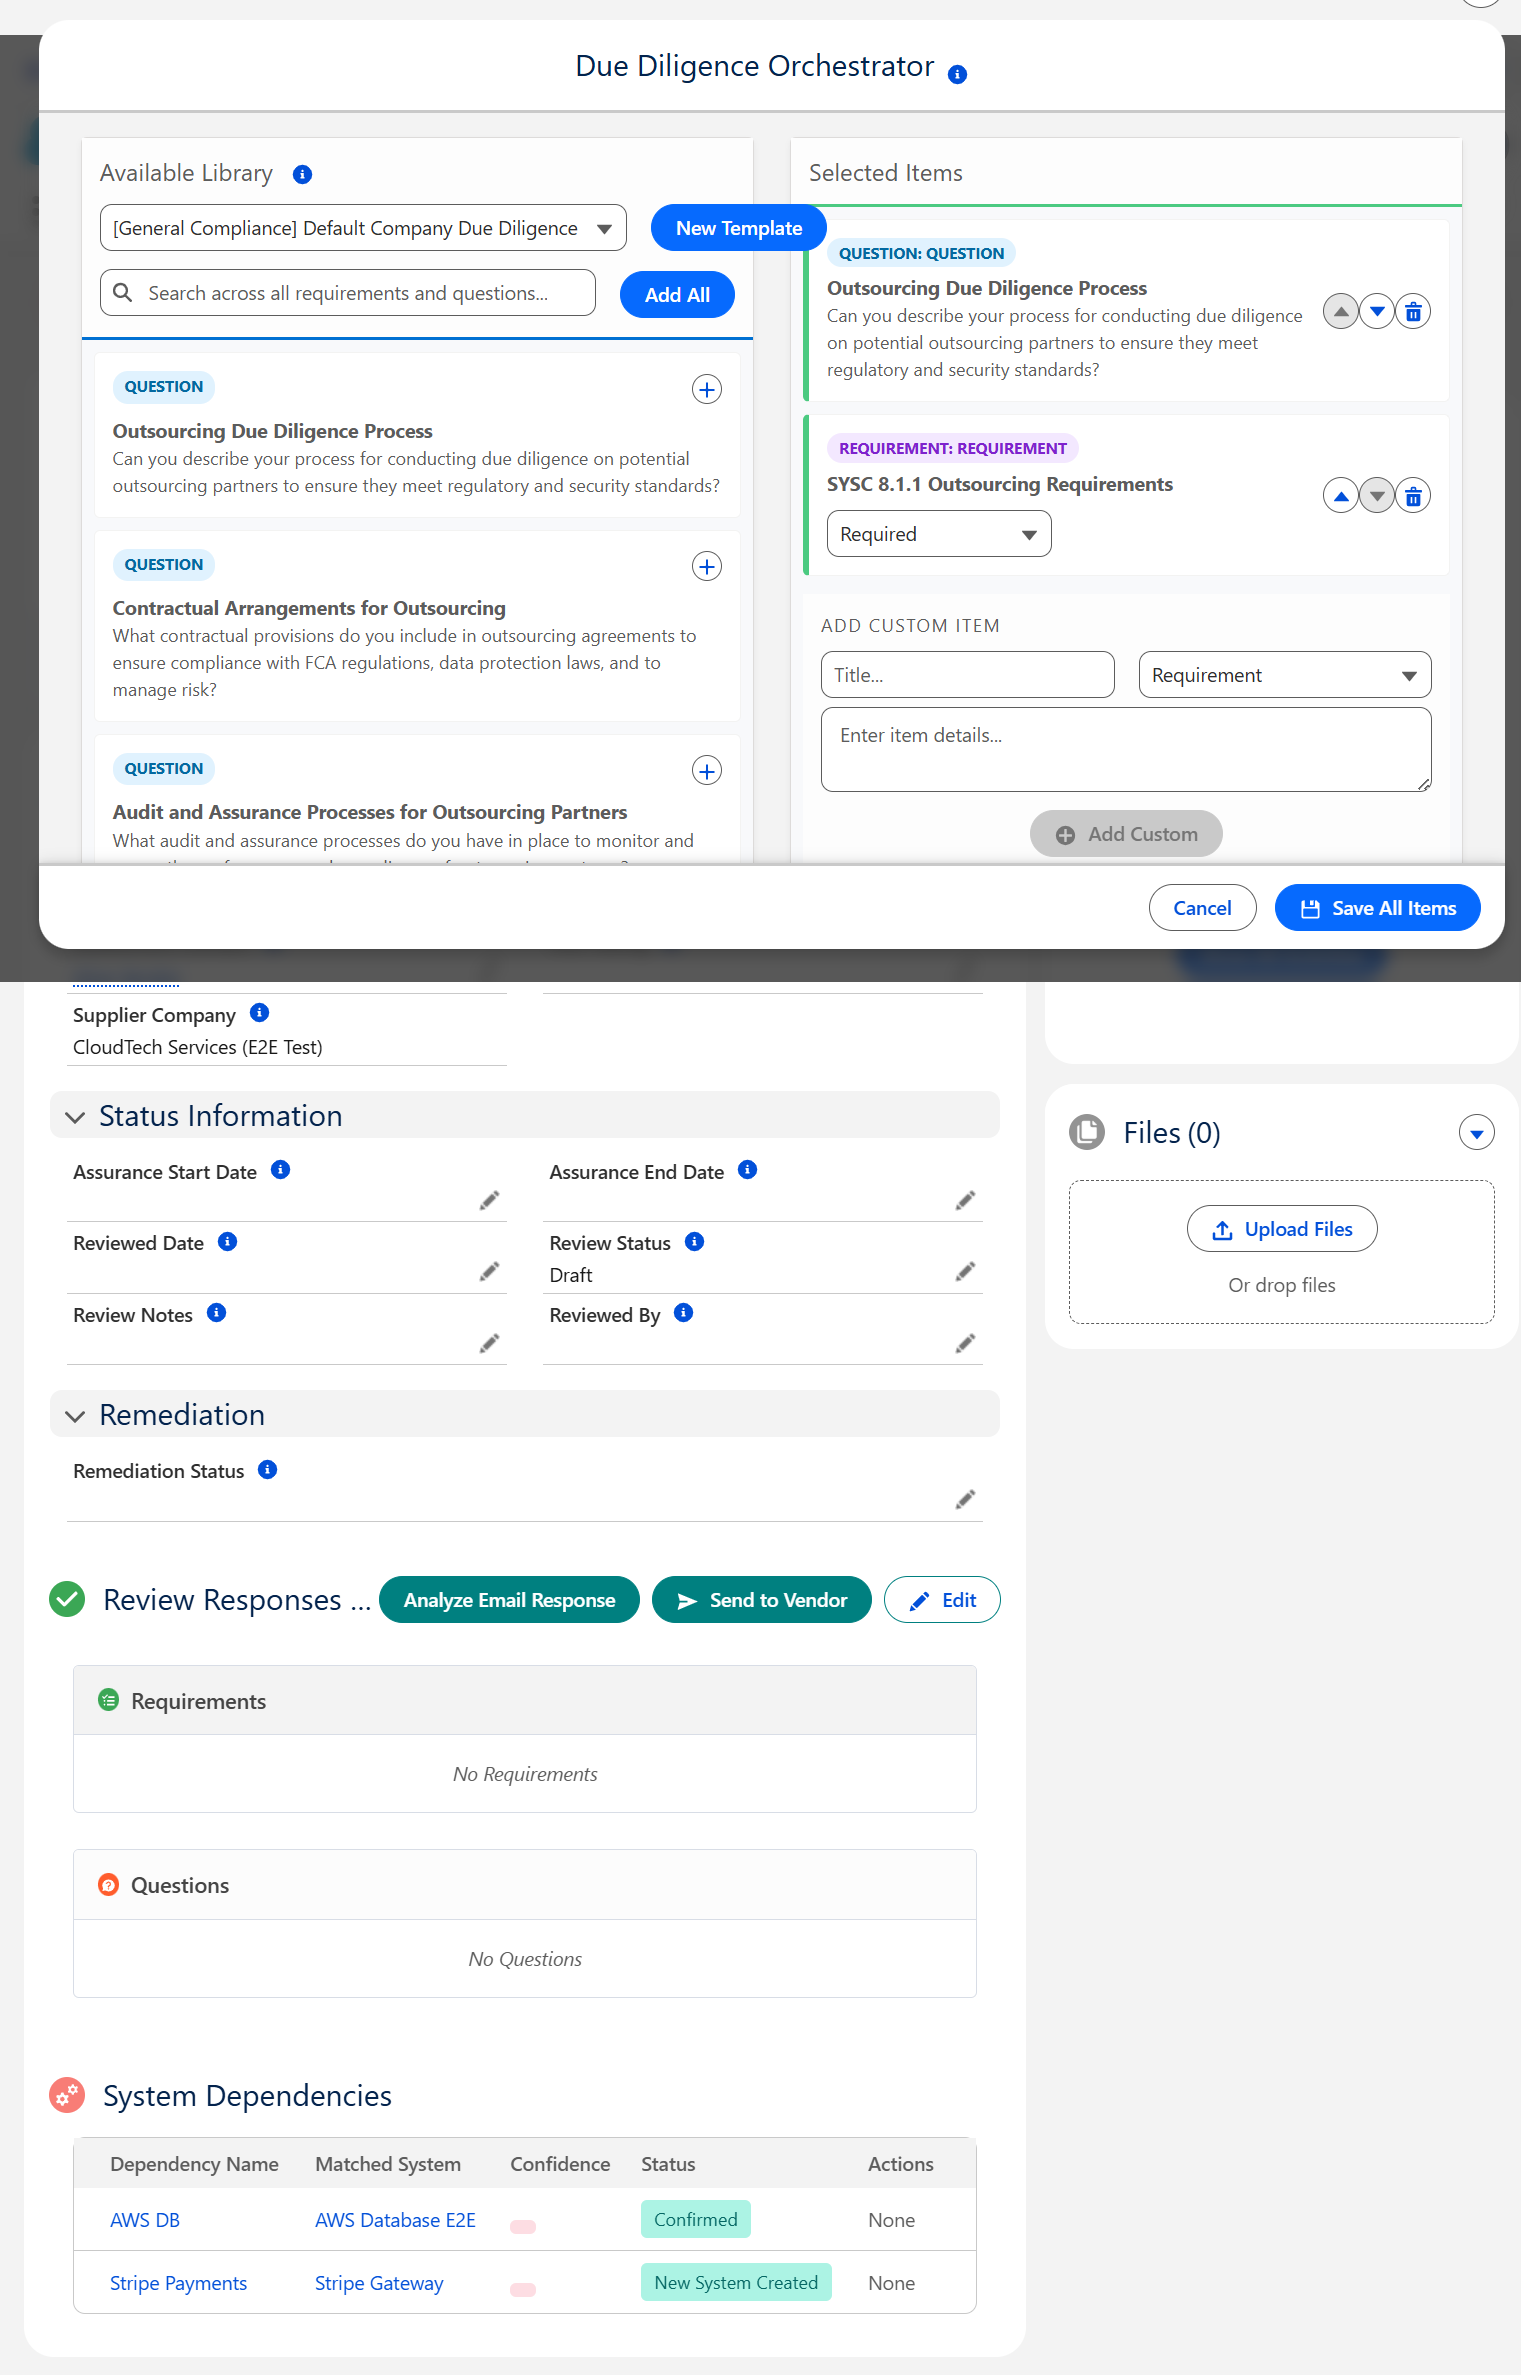
Due diligence support

Speed up supplier and third-party assessments with structured questionnaires and AI-assisted analysis against the minimum compliance you define.

AI guided horizon scanning
Due diligence orchestrator

Risk Framework consultancy

The right tool needs the right framework behind it.

Many risk programmes struggle because the method is unclear, not because the software is missing. Through our partners, you can get expert help defining the framework first, then embed it in DefinedGRC.

What a framework engagement can cover

  • ✓ Risk taxonomy and common definitions
  • ✓ Risk appetite and tolerance
  • ✓ Assessment methodology and scoring
  • ✓ Control framework and mapping
  • ✓ Governance, reporting and ownership
  • ✓ Business continuity approach

How it works

  1. Book a consultation. Tell us where your framework is today.
  2. Shape the framework. A partner works with your risk team on the method.
  3. Configure DefinedGRC. We install and tailor the package to match.
  4. Go live in your org. Your team works in the Salesforce they already know.
Book a Risk Framework Consultation

Built by people who have done the job.

We bring more than 25 years of experience in the financial industry, where risk management, process discipline, and operational resilience are non‑negotiable. Alongside this, we have extensive hands‑on experience designing and implementing Salesforce solutions, supported by Salesforce Cloud Consultant and Administrator certifications.

Across our careers, we've repeatedly seen organisations struggle to define and manage risk in a consistent, structured, and meaningful way. Too often, risk events and control assessments are logged vaguely or captured as narrative rather than insight. That leads to inefficient investigations and poor control design.

DefinedGRC is the tool we wish we'd had years ago: one that turns risk management from a reactive chore into a proactive, data‑driven capability, in the Salesforce platform your teams already use.

Need something unique?

We build custom objects and Lightning Web Components, with experience in highly regulated environments. If your process needs something the package does not do out of the box, we can build it.

Book a Risk Framework Consultation

Tell us about your risk team and where you are with Salesforce. We will talk through your framework, your process and the best route to get started.

Starting from scratch? You don't need a risk team to get started.

Many organisations begin before they have a formal approach to risk or resilience. DefinedGRC comes pre-configured with a ready-made process, so you have structure from day one. Our Risk and BCP partner can then help you build your approach and put it into practice, far faster than starting with a blank page.

info@definedGRC.com